How to Build an MCP Server for Your SaaS Product: Step-by-Step Guide
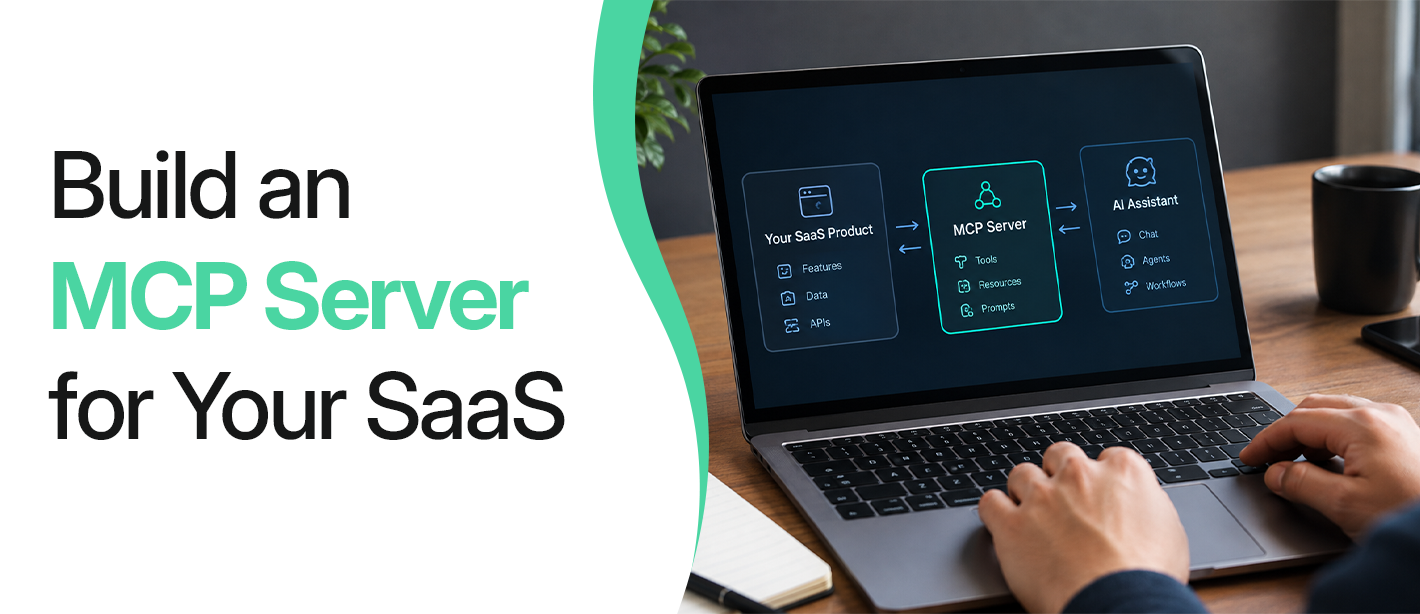

An MCP server lets compatible AI applications interact with your SaaS product, helping users complete tasks through the AI tools they already use. It also makes AI automation for SaaS workflows easier to extend beyond your product’s interface. To build these capabilities, expose selected backend operations as well-defined tools using an official SDK, enforce customer permissions, and test before deployment.
The ecosystem already has substantial activity. In December 2025, MCP maintainers reported over 97 million monthly SDK downloads and 10,000 active servers. These are dated ecosystem figures, not unique users or evidence of business ROI.
This blog shows you how to build MCP server support for a SaaS product on the latest Model Context Protocol spec.
Key takeaways
- An MCP server lets any MCP-compatible AI app use your product through one standard interface, instead of one custom integration per assistant.
- For SaaS, the default is a remote server over Streamable HTTP, protected by OAuth, with 3–5 task-level tools in v1.
- A focused first production version usually takes 3–6 weeks; auth and multi-tenancy take the most time.
What Is an MCP Server?
An MCP server is a service that exposes your product's actions and data to AI applications through the Model Context Protocol, an open standard that works like a USB-C port for AI. Once it is live, any MCP client (Claude, ChatGPT, VS Code, Cursor) can discover and use your product without a custom integration.
The request path is simple: AI app → MCP client → your MCP server → your existing API or database. Understanding how MCP connects AI applications to business systems helps you decide what your product should expose.
MCP vs API: How to Expose Your API to AI Agents
An API provides your application's existing operations. MCP adds a standardized interface through which AI clients can discover capabilities and call tools. Your web application backend can continue serving existing integrations while an MCP layer translates selected AI requests into API calls.
So the practical answer to how to expose your API to AI agents is a thin MCP layer in front of the endpoints you already have. Teams that have done CRM and third-party API integration will recognise the discipline; the difference is that your "developer" is now a language model.
Why Build an MCP Server for SaaS in 2027?
AI assistants are becoming a front door to software, and an MCP server for SaaS puts your product inside the tools customers already have open. The shift is measurable: Honeycomb says nearly 20% of its monthly interactive queries now come from agents, according to the 2026-07-28 release notes. Products that are easy for agents to use also collect the kind of usage data that shows measurable ROI from custom AI.
Before You Build: 4 Decisions for Product Teams
1. Choose Local or Remote Access
Use stdio when the client launches a local server process. Choose Streamable HTTP when customers need a hosted, remote MCP server. Both are standard MCP transports; select the deployment approach alongside your cloud infrastructure requirements.
2. Language
Match your backend. The official SDKs are TypeScript, Python, Go, and C#, all updated for the new spec. If your team is thin on either stack, you can hire a Node.js developer or bring in a dedicated Python developer for the MCP layer.
3. Design Authorization Early
Restricted customer data needs authenticated access and server-side permission checks. For supported HTTP authorization, follow MCP’s OAuth-based specification, including discovery and token validation. Add tenant and object-level checks rather than relying on tool descriptions to enforce security.
4. Decide Who Will Build and Maintain It
How to Build an MCP Server: Step-by-Step
Step 1: Define One Customer Workflow
Begin with “find unresolved billing tickets,” rather than exposing every endpoint. Translate the workflow into a small tool catalog and record acceptance criteria in a clear product requirements document.
Step 2: Initialize Your Project
With Python 3.10+ and uv installed, create the project below. This example follows the current Python SDK 2.x interface; preserve the resolved versions in uv.lock. Include upgrade ownership in your AI development process.
uv init saas-mcp
cd saas-mcp
uv add 'mcp[cli]>=2.0.0,<3'
Step 3: Implement Your First Read Tool
Save this as server.py. It assumes your sandbox supports GET /tickets?q=...&limit=... and returns a JSON object containing a tickets array. Adapt that contract to your API; backend integration is part of custom AI engineering.
Step 4: Connect Your SaaS Backend
Set SAAS_API_BASE to your sandbox HTTPS API and SAAS_API_TOKEN to a read-only credential using your local environment or secret manager. Start with uv run server.py. For systems spanning customer platforms, preserve the same access boundaries used in CRM integrations.
This demonstrates how to expose your API to AI agents: a discoverable tool calls an existing endpoint and returns selected fields. The credential represents one authorized sandbox context. A shared customer service needs per-request identity, safe upstream error mapping, and output validation before production.
Step 5: Add Resources and Prompts Selectively
Add a ticket resource when clients need reference data, or an incident-summary prompt when users need a reusable template. Support varies by client, so validate capabilities against the AI workflow you intend to deliver. Tools alone can be sufficient for the first release.
Step 6: Enforce Authorization and Tenant Isolation
For restricted HTTP access, implement the specification's OAuth-based flow, including protected resource metadata, discovery, PKCE, and access-token validation. Validate audience, issuer, expiry, and scopes; address JWT validation vulnerabilities when your provider issues JWTs.
Step 7: Add Safe Write Operations
Implement create_ticket through your backend with tickets:write permission and an idempotency key, so retries return the original result. Require confirmation for actions whose consequences warrant it. Keep permissions enforced in code; this is essential for dependable business automation, even if malicious instructions appear inside retrieved tickets.
Step 8: Test Tools and Actual AI Behavior
Launch MCP Inspector with npx @modelcontextprotocol/inspector, then configure a stdio connection using uv with arguments run server.py from the project directory. Test tool discovery, a valid query, invalid limits, and upstream failures before connecting an AI host. Consistent development workflows make these checks repeatable.
For the remote implementation, also test expired tokens, missing scopes, cross-tenant IDs, and duplicate writes. Ask the target client to “find open billing tickets”; verify both tool selection and permissions. Record client versions and expected results without labeling unmeasured performance as proven.
Step 9: Deploy Your Remote MCP Server
To understand how to deploy MCP server functionality, separate local stdio execution from network hosting. Configure the SDK's Streamable HTTP transport and deploy an HTTPS /mcp endpoint through a container or managed application platform. Establish health checks, secret management, and rollback with managed cloud operations.
Protect the endpoint before public access, validate Origin according to the transport specification, and confirm proxy behavior for JSON and SSE responses. Run an authenticated remote smoke test and an unauthorized rejection test. Follow the Streamable HTTP requirements, using SDK defaults compatible with your target clients.
Step 10: Pilot, Monitor, and Improve
Track tool latency, failures, throttling, and completed workflows. Log user, tenant, tool, and correlation IDs while redacting credentials and sensitive payloads. Evaluate measurable AI business value through successful customer tasks, then refine descriptions and permissions before expanding access.
MCP Server Security Checklist
An MCP server is a new, AI-driven entry point into customer data, so it needs the same contextual AI governance as any agent system.
- Scope tokens per tool and keep read and write scopes separate.
- Confirm destructive or paid actions with the user. Supabase now uses Multi Round-Trip Requests to show a project's cost or a delete query before acting.
- Enforce permissions in your API or database, never only in a tool description.
- Treat tool inputs and fetched content as untrusted, since text in a ticket or document can carry prompt injection.
- Validate business rules beyond the schema, and rate-limit per user and tenant.
- Keep an audit log of every tool call and let users revoke access.
Common Problems and Production Checks
Use the following checks during your release process.
Before launch, verify those controls plus rate limits, sanitized errors, revocation, audit logs, and rollback. Version tool contracts separately from protocol compatibility and document breaking changes.
Real-World SaaS MCP Server Examples
What Does an MCP Server Cost?
The biggest cost drivers are auth and tenant isolation, not tool code. Timelines assume a clean API; legacy systems add time, which is why many teams hire remote AI developers for the first release.
Conclusion
To build MCP server support that lasts, start with five task-level tools, write descriptions a model can act on, put OAuth and tenant checks in every handler, and deploy statelessly on Streamable HTTP. Teams that build on the 2026-07-28 spec now skip a painful migration later.
If you want a second pair of eyes on your tool design or auth model, book a free discovery call with Amrood Labs, or bring in dedicated developers to ship the first release with your team.
Frequently Asked Questions
Is the Model Context Protocol only for Claude?
No. Anthropic introduced MCP in November 2024, but it is an open standard now run as a Linux Foundation project. Claude, ChatGPT, VS Code, Cursor and many other clients support it, so one server reaches all of them.
Should I build my MCP server in Python or TypeScript?
Use the language your backend already runs. Both official SDKs are at v2 and support the 2026-07-28 spec. Python needs the least boilerplate; TypeScript fits Node.js and Next.js stacks and serverless hosting.
Is HTTP+SSE still supported in 2027?
It still works for backward compatibility, but it has been deprecated since 2025-03-26 and is on a formal removal path. Build new remote servers on Streamable HTTP with the stateless 2026-07-28 protocol.
Can one remote MCP server serve all my customers?
Yes, if it is multi-tenant. Each request carries the user's OAuth token, and the server resolves the tenant and permissions from that token on every call. Never route all customers through one shared key; tenant isolation is a core part of multi-tenant cloud app development.
How long does it take to build an MCP server for SaaS?
An MVP with a few read-only tools takes 1–2 weeks. A production server with OAuth, multi-tenancy and monitoring usually takes 3–6 weeks, following the same stages as any custom AI development process.
Table of Content
Share Now